~/blog/who-can-read-your-household-budget-budgetstack-threat-model
Who can read your household budget: a threat model for BudgetStack
BudgetStack's threat model, adversary by adversary: what a stranger, another household, a stolen database, the OCR model and the operator can and cannot read.
Every budgeting app has the same sentence on its landing page: your data is encrypted, often with "bank-grade" in front of it. The sentence is true for nearly all of them and tells you nearly nothing. It does not say who holds the key, what stays readable, or whom the encryption is meant to stop. TLS on the wire and an encrypted disk at the hosting provider qualify. So does a design in which the operator cannot read anything at all. Those are very different products wearing the same badge.
BudgetStack is the household budget app I build and run. It reads receipts, imports bank statements, matches one against the other, and shares the result between the people in one household. That makes it a store of exactly the data a household would least like to see leaked: where you shop, whom you pay, what comes in each month. This article is its threat model, written adversary by adversary. It covers why the server has to see your data at all, how a stranger is kept from learning that you have an account, how Postgres keeps one household out of another, what someone holding a copy of the database can and cannot read, what the model reading your receipt is allowed to keep, and what stands between your data and me.
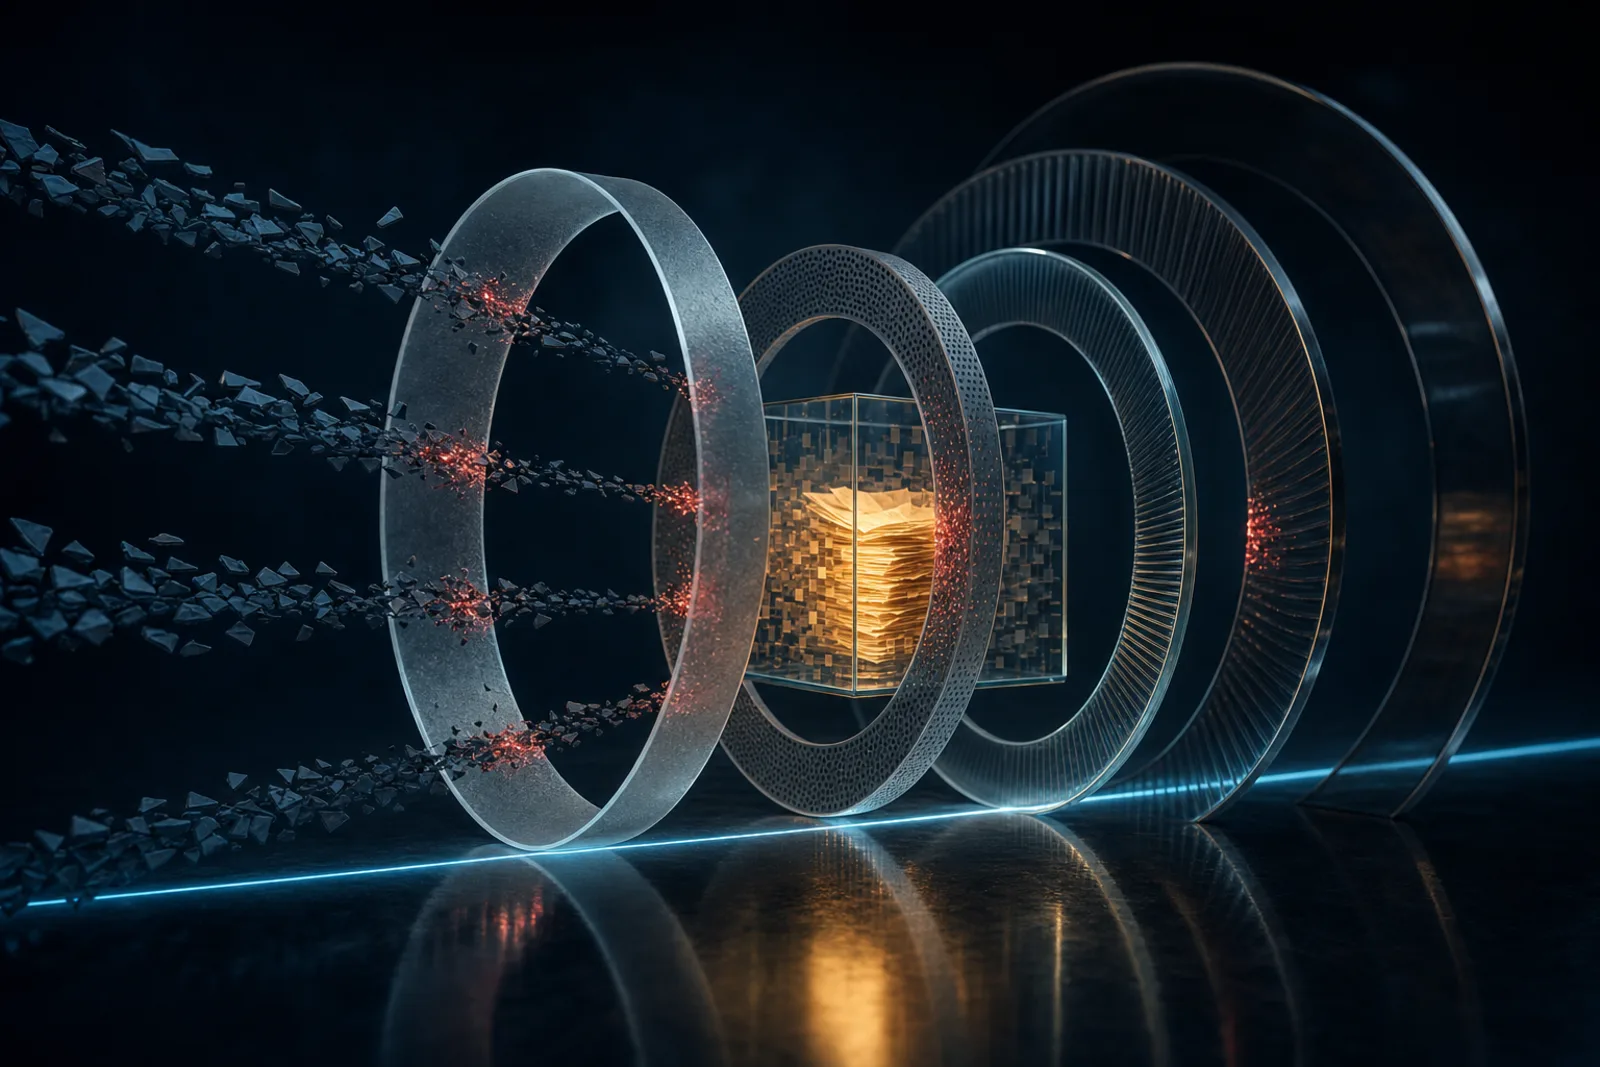
Each ring stops a different adversary at a different distance. The receipts in the middle are readable only from inside the cube, and the cube is where the server sits.
The design is public, the operational details are not#
Kerckhoffs put it in 1883: a system should stay secure when everything about it except the key is known. A design that is safe only while nobody knows it is not safe. So this article names the algorithms, the shape of the key hierarchy and the reasons behind each fence, the same things already listed on my projects page.
A rate limit is the opposite case. Publishing its exact threshold hands a script its pacing. The same goes for where keys are stored, how the infrastructure is laid out, what the schema calls things, and which alerts fire at what number. None of that is here, and its absence is deliberate. If a paragraph below feels a step vaguer than the rest of this blog, that is the reason.
One more scope note. This is the threat model of the web application at app.budgetstack.pl. The phone app and the browser extension that imports retailer receipts have their own surfaces, and they are not covered here.
Draw the line first: the server has to see your data#
The strongest privacy design for a budget app is end-to-end encryption: keys exist only in the members' browsers, and the server stores blobs it cannot open. I considered it for BudgetStack and declined it. The reason is the product itself.
Almost everything BudgetStack does for you happens on the server. A model reads the receipt photo. The statement importer parses your bank's export. A matcher pairs a receipt with the card payment that paid for it. Recurring payments are detected across months. Totals are summed, and a weekly digest is mailed while you sleep. Every one of those steps needs the plaintext. Moving them all into the browser would mean a much weaker product, or one that only works while a tab is open.
So the honest label is encryption at rest with server-held keys. Not end-to-end. That choice sets the boundary for everything that follows:
Everything to the right of the API sees either ciphertext or the minimum it needs. The API itself sees everything, because it does the work. Each adversary below is placed somewhere on this picture.
A stranger with a list of email addresses#
The cheapest attack on any account system needs no exploit. You take a list of addresses and ask the registration form about each one. Most apps answer honestly: "an account with this address already exists". That answer is a leak. It tells a stranger which of those people keep their household budget here, and that alone is enough to build a convincing phishing mail.
BudgetStack used to give that answer. On 2026-10-30 a wave of bot registrations arrived, all of them left unconfirmed. They never got anywhere near anybody's data, because every new registration gets its own empty household behind the same fence as everyone else. They did show me what the form was disclosing.
Registration now answers the same way whether the address is new or taken, and it signs nobody in. A new address receives a confirmation code. A taken address receives a short mail saying somebody tried to register with it, at most once a day, so the form cannot be used to flood an inbox. An account only becomes usable when the code comes back together with the password. The password is what stops six digits from being a way into an account. It also means a person who registered a stranger's address cannot be the one who confirms it.
The rest of the front door is unremarkable on purpose: a captcha that stays invisible unless the visitor looks automated, rate limits on every authentication route, and automatic removal, after a week, of accounts that were never confirmed and barely used. A response-time difference between the two registration paths still exists. The captcha and the limits make it impractical to measure. Impractical is not impossible.
Another household on the same database#
All households live in one Postgres database. The usual way to keep them apart is a WHERE household_id = ? in every query. That works until the one query somebody forgot. In a codebase where sign-in, account deletion, mail and the shared product catalogue all need to step outside a single household, "somebody forgot" is a matter of time.
BudgetStack uses Postgres row-level security as the fence instead. Each request runs inside a transaction that names one household, and the database itself refuses to return rows that belong to another. Application code can still have bugs. The bug just cannot read the neighbours' money.
Two details made this work in practice.
- Not every table gets the same fence. Account and session tables have to be reachable outside a household, at sign-in for example. Financial tables never are. No exception the application can switch on reaches receipts, statements or budgets.
- References carry the household too. Postgres checks a foreign key without row security, so a fence on rows alone would still let a receipt line point at another household's receipt. Every reference between financial tables therefore includes the household, and the database rejects a cross-household link.
The first draft of that migration had an exception for the schema owner. In the way production is configured, that exception would have opened every table there. A test suite that runs the fence against a real Postgres set up like production caught it before deploy. Tests against an idealised database would not have.
There is one deliberate crossing. Product names on receipts are cryptic ("MLEKO UHT 3,2 1L"), and the catalogue learns readable names from what households confirm. A name typed by one household is that household's own words, though. With open registration, anybody can upload a crafted receipt to fish for them. So a learned name only surfaces once other households have independently given the same answer, and it never carries the identity of anyone who gave it.
Someone holding a copy of the database#
Row-level security fences out bugs. It does nothing against a person who has the database itself: a leaked backup, a snapshot of the storage bucket, a misconfigured replica, an SQL console in the wrong hands. For that adversary the data has to be unreadable without keys they do not have.
Every household gets its own random data key. That key is wrapped by a master key that is never stored in the database, so a dump contains only the wrapped form. From the household key, two working keys are derived: one encrypts, one builds lookup indexes. Encryption is AES-256-GCM, and the household's identity is bound into each ciphertext as associated data.
A simplified version of sealing one value, not the production code:
import { createCipheriv, randomBytes } from "node:crypto";

export function seal(plain: string, key: Buffer, householdId: string): string {
  const iv = randomBytes(12);
  const cipher = createCipheriv("aes-256-gcm", key, iv);
  cipher.setAAD(Buffer.from(householdId)); // binds the ciphertext to its owner
  const body = Buffer.concat([cipher.update(plain, "utf8"), cipher.final()]);
  return Buffer.concat([iv, cipher.getAuthTag(), body]).toString("base64");
}
The associated data is the part that is easy to skip. Separate keys already mean a value copied into another household's row will not open under that household's key. The binding covers the mistake separate keys cannot: a bug that loads the wrong household's key for a request. Without the binding, a value copied across would open and be served in the wrong context. With it, the authentication tag fails and the value refuses to open. Two locks, each covering a mistake the other cannot.
What is sealed, and what is not#
Sealed: transaction descriptions, counterparties, notes, account labels, merchant names and tax IDs, the last four card digits printed on a receipt, every receipt line, product names, document filenames, and every file in object storage. Files are sealed by the API before they are stored. There is no longer any upload path that writes plaintext to the bucket.
Not sealed: amounts, dates, currencies, category names, and the bank's own transaction-type codes. Totals and filters run in SQL on those columns, and summing ciphertext is not something AES-GCM does. Concretely, someone with a dump learns that a household spent 312.40 PLN on a given Tuesday in a category called "Groceries". They do not learn the shop, the city, or what was in the basket. That is not nothing. I would rather say so than imply the dump is blank.
Matching on data you cannot read#
Encryption breaks equality. AES-GCM with a random IV turns the same description into a different ciphertext every time, so "find the statement line with this counterparty" stops working. The standard answer is a blind index: a deterministic fingerprint stored next to the ciphertext. The fingerprint has to be keyed, though:
import { createHash, createHmac } from "node:crypto";

// BAD: anyone holding the dump can hash "BIEDRONKA 1234 KRAKOW" and find every matching row.
const weak = createHash("sha256").update(description).digest("hex");

// GOOD: without the household's index key, the column is noise and cannot be confirmed offline.
const blind = createHmac("sha256", indexKey).update(description).digest("hex");
The unkeyed version looks harmless because a hash is "one-way". Card descriptions are not secrets, though. They are short, repetitive and guessable, and a guessable input turns a hash into a lookup table. The keyed version gives the application equality and the dump nothing. The difference between encoding, hashing and encryption is its own topic, and I wrote about it separately.
Leaving means leaving#
When the last member leaves a household, its data key is destroyed. Amounts and dates stay for aggregate statistics. The household's own words become permanently unreadable, in every backup taken before that moment too, without hunting for those backups. That is crypto-shredding, the same pattern I described for event-sourced systems, applied to an ordinary relational schema.
The rehearsal that sealed everything with one key#
Existing data had to be encrypted in place, with the application stopped. The first rehearsal, on a clone of the development database, sealed every household's rows with the first household's key. The migration connected as a database superuser, row-level security does not apply to superusers, and the script trusted the fence to scope each query. The fence was not there.
The script now names the household in every query instead of relying on row security, and it fails unless every sealed value opens with its own household's key. The final rehearsal ran twice, the second run finding nothing left to do. All 26 read endpoints answered with no ciphertext in any response, and the spending totals matched the old values to the grosz. The lesson is narrow. A fence that protects the application does not protect the tools that maintain it.
The model that reads your receipt#
Reading a crumpled receipt photo well takes a capable model. BudgetStack started with a local one and moved to a hosted one, which means the receipt image leaves the house.
Every such request asks the routing layer for endpoints that keep no data and do not collect it for training. A model without such an endpoint is not a fallback case: the call fails. When I change models, I check that the new one is still served under those terms before it goes live.
The scope of that guarantee is narrow, and it should be stated. Zero data retention is a contractual promise of the provider. I can choose providers that make it and refuse those that do not. I cannot verify cryptographically what happens on their side. The image is sent; the promise is about what they do with it afterwards.
Someone who has your password#
Passwords leak through reuse more than through anything a server does. The defences here assume your password will eventually be in someone else's hands.
- A second factor. Time-based one-time codes are optional and switched on in account settings. A wrong code and a missing code are reported only after the password has checked out, so the prompt tells a stranger nothing. Sign-in through Google or Apple relies on their second factor rather than adding another.
- Changing the password ends other sessions. Every device except the one making the change is signed out, and so is every device after a password reset. Every session is a row you can see and revoke.
- The full export is audited and rate-limited. It is the one call that hands over a whole history, so it is the one a stolen session makes. Each export is logged with who took how much.
- API keys are read-only. A key for scripts can read, cannot write, and cannot take the full export.
- A backup never carries the household key. The owner's export is complete and decrypted: it is your data, and portability is a promise. It does not contain the key that opens your stored files, so a stolen export plus access to the storage bucket still does not open your documents.
None of this stops someone who has both your password and your phone, or malware on the device you use the app from. Nothing a server does can.
Me#
The adversary I can defend against least is the person running the server. The API process holds the keys, because it does the work. Code running inside it can read what it serves. That includes code I write.
What I could do structurally, I did. The admin panel is a separate application with separate accounts that the product's account code cannot create. It requires a second factor without exception and is fenced off at the network edge. It has no endpoints on the public API for anyone to find. Every change made through it is written to an audit log with before and after values. It shows households as counts, not contents: no receipt, statement line or transaction is ever loaded by the panel.
That limits accidents and narrows a breach of the panel. It does not stop the operator from deploying different code. What stops that is not cryptography. It is a business model that charges for the product instead of selling the data, written on the landing page, and an architecture that would make breaking that promise a deliberate act rather than a side effect. You have to trust me on the first part. The second part is what this article is for.
What the encryption costs me#
Encryption at rest is not free, and the costs are worth naming next to the benefits.
- Search filters after decrypting. SQL narrows by what it can still see, the rows are opened, and the text filter runs in the application. At household scale this is fast. Somewhere past tens of thousands of rows per household it will need a tokenised index instead, and that is marked in the code as a known shortcut.
- Silent failure modes. A hand-written query that selects a sealed column without passing it through the opener returns ciphertext. An equality check against one never matches. The type checker catches neither. Checking that no response contains ciphertext is the guard, and it has to be done on purpose.
- The master key becomes the single most important secret. Losing it loses every household's data. Leaking it undoes most of the section above. Both failure modes sit on one value.
- Some work moves earlier. Rules that used to read descriptions at query time, such as "is this a transfer between my own accounts", now run when a row is written and are stored as flags. Changing a rule means recomputing the flags.
The model on one page#
| Adversary | What they can learn today | What stands in the way | Where it stops |
|---|---|---|---|
| Stranger with addresses | Nothing about who is registered | Identical answers, captcha, rate limits | Timing analysis, made impractical |
| Another household | Nothing | Row-level security, household-scoped references | A compromised server process |
| Copy of the database | Amounts, dates, categories | Per-household AES-GCM, keyed blind indexes | Possession of the master key |
| Receipt model provider | One receipt image per request | Zero-retention routing only | The provider's own compliance |
| Holder of your password | What you can see | Optional second factor, revocable sessions, audited export | Password plus phone, or a compromised device |
| The operator | Anything the server can read | Separate admin app, counts not contents, audit log | Deployed code, and trust |
Questions to ask any budget app, including this one#
A threat model is useful beyond one product if it turns into questions. These are the ones I would ask before trusting any app with a household's money, and BudgetStack has to answer them too.
- Who holds the encryption key, and is it stored next to the data it protects?
- What stays readable in a database dump, and why that and not more?
- Does the registration form tell a stranger whether an address has an account?
- What does the model reading my receipts keep, and what happens if no zero-retention option is available?
- What can the operator's admin panel display, and is that logged?
- When I leave, what becomes unreadable, and does that include old backups?
BudgetStack is at app.budgetstack.pl, with a free plan, in Polish. If you find a gap in anything above, write to budgetstack@stackmade.pl. A report of a hole I did not know about is worth more to me than a signup.
$ related posts
· 20 min
Securing Event-Sourced Financial Systems
Part 4 of an event sourcing series: PII kept out of events, crypto-shredding for GDPR erasure, locked-down CQRS projections, and auditable observability.
20 min
· 8 min
Encryption, Encoding and Hashing Are Not the Same Thing
Learn how encryption, encoding, and hashing can secure your data. Explore examples and differences between these essential techniques.
8 min
· 17 min
Event Sourcing Behind the Port You Already Have
Event sourcing in Symfony 8: an event-sourced repository swapped in by one DI alias, proven by the same contract test, and what the alias did not cover. Part 5.
▸ DDD, CQRS and Hexagonal Architecture in Symfony 8 · 5#ddd#hexagonal-architecture#symfony#php#event-sourcing#postgresql#cqrs17 min